Privacy policy template notes for marketplaces founders
Your marketplace connects buyers and sellers, or users and service providers, and handles sensitive personal data every day. A privacy policy isn't just legal p
Photo by Markus Winkler from Pexels
Lead
Your marketplace connects buyers and sellers, or users and service providers, and handles sensitive personal data every day. A privacy policy isn't just legal paperwork; it's a promise to your users about how you collect, store, and protect their information. Without a clear, honest privacy policy, you risk losing customer trust, facing compliance fines, and attracting regulators. This guide walks you through building a privacy policy template tailored to marketplace-specific challenges: user data across multiple parties, third-party integrations, payment processing, and compliance across jurisdictions.
TL;DR
- A privacy policy explains what data you collect (names, emails, payment info), why you collect it, and how long you keep it.
- Marketplace-specific clauses must cover seller profiles, buyer anonymity options, payment processor data sharing, and dispute resolution.
- Use a template as your starting point, but customize it for your actual data flows, generic policies attract regulators and undermine user trust.
- Include clear opt-out options for marketing, cookie consent for tracking, and data deletion requests under GDPR/CCPA.
- Audit your policy annually or whenever you add a new feature (like AI recommendations or seller analytics).
Why marketplace privacy policies are different
Your privacy policy isn't just about you. Unlike a simple SaaS app, a marketplace processes data on behalf of multiple parties: buyers, sellers, payment processors, shipping partners, and possibly review platforms. Each of these relationships creates new data-handling obligations.
Key takeaway: Marketplace privacy policies must clearly separate who owns user data and who is responsible for protecting it at each stage of a transaction.
When a buyer makes a purchase on your platform, your marketplace:- Collects their email, shipping address, and payment method
- Shares some of that data with the seller (so they can fulfill the order)
- Passes payment details to a payment processor (Stripe, PayPal, etc.)
- May retain anonymized behavior data for analytics and recommendations
- Could face liability if any third party misuses that data
"48% of users have stopped buying from a company over privacy concerns.">, Privacy Policy Template for Websites and Apps (and Examples)
This statistic underscores why transparency matters. Users vote with their wallets. A marketplace with a sloppy or evasive privacy policy loses credibility instantly.
Core sections every marketplace privacy policy needs
1. Data collection: What you actually gather
Start with an honest inventory. Your privacy policy should list every data point you collect:
- Identity data: name, email, phone, date of birth (for age verification on restricted items)
- Address data: shipping address, billing address, saved locations
- Payment data: credit card (if stored), purchase history, refund requests
- Device data: IP address, browser type, device ID, cookies (even if you don't use them yet)
- Behavior data: pages visited, time spent, search queries, items wishlisted, reviews written
- Communication data: support emails, chat logs, feedback submissions
- Seller-specific data: business registration, bank account (for payouts), tax ID, inventory counts
- Location data: GPS coordinates if you offer location-based services
2. Purpose & legal basis: Why you collect it
For each data type, explain the legitimate interest or legal reason. Under GDPR and CCPA, consent alone isn't always enough, you need a legal basis. Common ones:
- Performance of a contract: You need the shipping address to deliver the order.
- Legal obligation: Tax authorities require you to retain transaction records.
- Legitimate interest: You analyze buyer behavior to recommend products (balanced against user privacy rights).
- Consent: You ask users to opt-in to marketing emails.
3. Third-party sharing & data processors
List every vendor that touches user data:
- Payment processors (Stripe, PayPal, Square)
- Email marketing platforms (SendGrid, Mailchimp)
- Analytics tools (Google Analytics, Mixpanel)
- CDNs and hosting providers
- Customer support platforms (Zendesk, Intercom)
- Fraud detection services
- Sellers (they receive buyer name, address, and contact info)
- What data they receive
- Where they process it (country/region matters under GDPR)
- For how long they retain it
- Their own privacy policy link (users should be able to trace data downstream)
4. User rights & deletion
Under GDPR (EU), CCPA (California), and similar laws, users have the right to:- Access: Download all their data in a portable format
- Correction: Fix inaccurate information
- Deletion: Request you erase their data (with exceptions for legal holds)
- Opt-out: Stop marketing and behavioral profiling
- Portability: Export their data to competitors
- How users submit these requests (email, account settings link)
- Your response timeline (usually 30 days)
- Any exceptions (you must retain transaction records for tax law)
- Cost (free for users; you can't charge)
5. Data retention: How long you keep it
Be specific. Vague language like "we keep data as long as necessary" doesn't satisfy regulators. Instead, map retention periods:
| Data Type | Retention Period | Reason |
|---|---|---|
| Active user account data | Duration of account + 30 days after deletion | Service delivery |
| Transaction records | 7 years | Tax/audit requirements |
| Marketing emails (opt-out list) | 3 years | Compliance with unsubscribe requests |
| Fraud detection logs | 1 year | Dispute resolution & investigation |
| Cookies (non-essential) | 13 months | Analytics & retargeting (varies by law) |
| Support chat logs | 2 years | Customer service & dispute reference |
6. Cookie & tracking transparency
If you use Google Analytics, Facebook Pixel, Hotjar, or any tracking pixel, you must disclose it in your privacy policy and provide a clear, pre-checked cookie banner on first visit (GDPR requirement). Many marketplace founders bury this in vague language or forget the opt-in toggle entirely.
Your policy should list:- Essential cookies (session ID, CSRF tokens), always on
- Analytics cookies (Google Analytics), requires consent
- Marketing cookies (retargeting pixels), requires consent
- Third-party cookies (partner widgets), requires consent
Building your privacy policy: Step-by-step
Step 1: Inventory your data flows
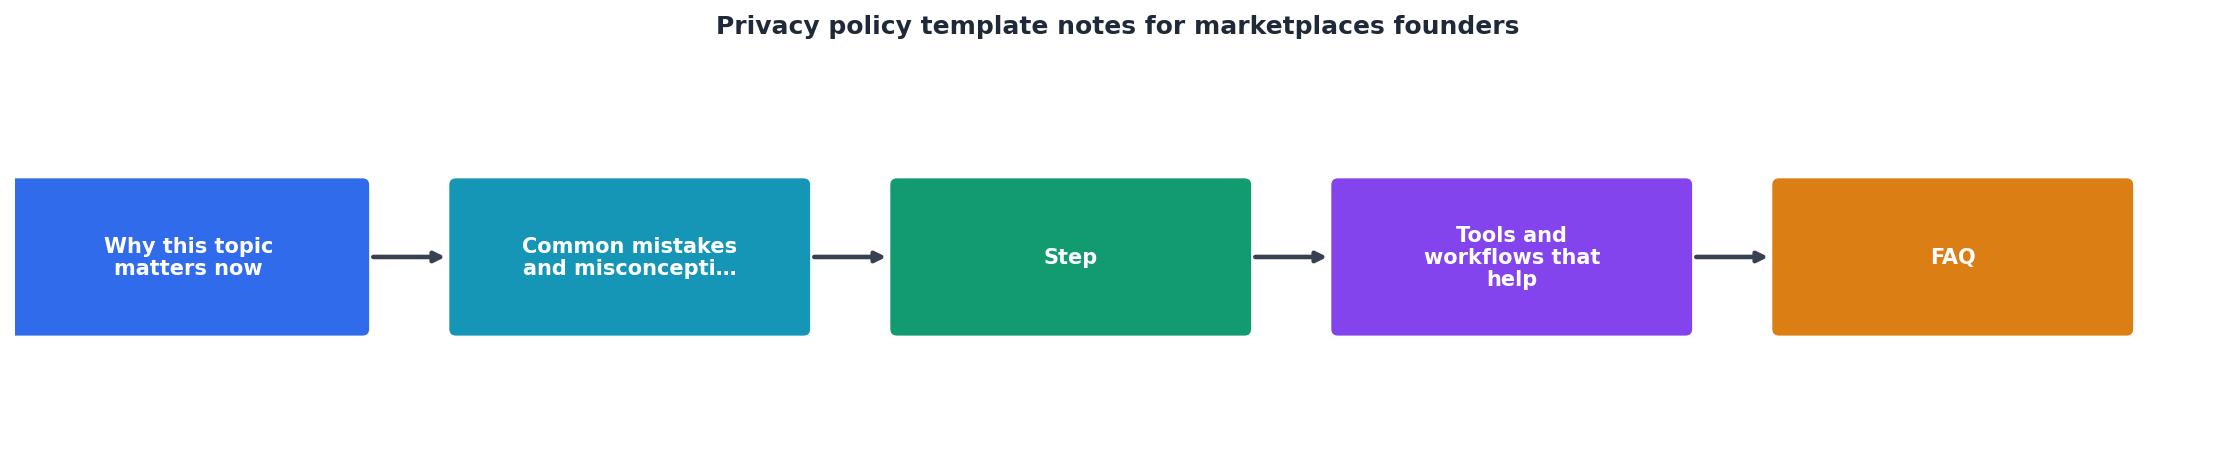
Before writing a single sentence, map every place user data flows:
- Your database (where you store it)
- Third-party services (who processes it)
- Seller accounts (what they can see)
- Backups and disaster recovery (how long retained)
- Logs and analytics tools (what's tracked)
- Payment processors and gateways
- Communication platforms (email, SMS, chat)
Step 2: Choose a template and customize
Start with a reputable template (Termly, Iubenda, or your lawyer's template). Do not copy a competitor's policy, it's likely wrong for your marketplace too. Templates often include generic placeholder text; replace every placeholder with your actual data practices.
Step 3: Run through the compliance checklist
Privacy Policy Compliance Checklist
Your progress is saved automatically in your browser.
Step 4: Get legal review (if you're outside the US)
If you serve EU users, GDPR compliance isn't optional, it's a €20 million fine or 4% of global revenue, whichever is higher. A 30-minute consult with a privacy lawyer is cheaper than that risk. Same for CCPA (California), which applies even if your company is outside California.
Step 5: Publish and announce the change
Add your privacy policy to your website footer and make it easy to find. If you significantly change your policy (especially new data uses), email users and give them 30 days to review before the changes take effect. This builds trust and shows good faith.
Marketplace-specific red flags to avoid
Auto-renewal hidden in privacy policy: Don't bury renewal terms in your privacy policy. Separate them clearly in your Terms of Service. Under ROSCA (US) and similar laws, explicit consent for each renewal is required.
Seller data as a separate product: If you plan to sell anonymized seller insights to competitors, disclose this upfront in your policy, don't add it later via an update. Sellers should know their data could become a revenue stream.
Undisclosed AI training: If you use user data (reviews, chat logs, product descriptions) to train machine-learning models, say so explicitly. Users are increasingly sensitive to AI data use. Terms Doctor's 101 checks include "AI training on user data without clear consent", this is a red flag for many.
Cross-border data transfers without safeguards: If you're a US company serving EU users, you can't just "transfer to the cloud." You need Standard Contractual Clauses (SCCs) or another legal mechanism. Schrems II ruling tightened this; many companies got it wrong.
No data deletion for sellers: Sellers should be able to request that their inactive listings are deleted. A policy that says "we keep all data forever" signals you see user data as an asset, not a trust responsibility.
Using Terms Doctor to check your privacy policy
Once you've drafted your policy, paste your Terms of Service and Privacy Policy into Terms Doctor. The extension runs 101 consumer-protection checks, including:
- Forced arbitration clauses (blocks user lawsuits)
- Auto-renewal without clear opt-out
- Undisclosed data sales to third parties
- Lack of GDPR-compliant deletion rights
- Seller data not properly segmented from buyer data
- Hidden fees or dynamic pricing
FAQ
Frequently Asked Questions
Next steps: Protect your marketplace and users
A privacy policy is a living document, it reflects how your marketplace actually works, not how you hope it works. Users and regulators will hold you accountable to every word.
The free Terms Doctor extension helps you spot privacy risks in any ToS or privacy policy (your own or competitors'). It grades policies A–F and flags 101 common loopholes, forced arbitration, hidden auto-renewal, undisclosed data sales, and more. Use it to validate your draft policy before launch, and audit annually as your marketplace grows.
Remember: a clear, honest privacy policy isn't a burden, it's competitive advantage. Users choose marketplaces they trust. Show them you respect their data, and they'll come back.
Additional Resources
- Privacy Policy Template for Websites and Apps ... - Download our free privacy policy template for your website or app and learn how to fill it out properly with examples.
- Privacy Policy for Startups & Developers Template - Designed specifically for app developers and indie hackers, this Notion document provides a clear, professional structure for outlining how you collect, use, ...
- Privacy Policy Template - A transparent and complete Privacy Policy agreement, which explains exactly what information a company collects and how it uses that information ...
Ready to Read Terms Before You Sign?
Terms Doctor finds terms of service on any site and grades them A-F in seconds.
Get Started“Terms Doctor flagged forced arbitration and AI training clauses in seconds. I finally know what I am agreeing to.”
Privacy-conscious shopper