Terms of service review checklist for B2B SaaS teams
When your team signs up for a new SaaS tool, whether it's a project management platform, analytics dashboard, or customer data tool, you're entering a binding l
When your team signs up for a new SaaS tool, whether it's a project management platform, analytics dashboard, or customer data tool, you're entering a binding legal agreement. Most teams skip the terms of service entirely, clicking "I agree" without reading a single word. That shortcut can cost you thousands in unexpected charges, expose your data to uncontrolled AI training, lock you into forced arbitration, or trap you in auto-renewal clauses designed to make cancellation nearly impossible.
A proper SaaS terms review protects your company, your data, and your budget. This checklist walks you through the most critical red flags your team should catch before signing any contract.
TL;DR
- Data ownership and AI training: Verify that you own your data and that the vendor won't use it to train AI models without explicit opt-in.
- Auto-renewal and cancellation: Confirm cancellation is simple, free, and doesn't require phone calls or manual form submissions.
- Liability limits and indemnification: Check whether the vendor caps their liability and what happens if they expose your data.
- Dispute resolution and arbitration: Watch for forced arbitration clauses that prevent you from suing or joining class actions.
- Price and change policies: Ensure price increases require notice and that you have a way to exit if terms change materially.
Why B2B teams skip terms reviews (and why they shouldn't)
Most teams treat terms of service as boilerplate, something legal wrote years ago and never changes. In reality, SaaS vendors update their terms regularly, often adding new clauses that benefit them and restrict your rights. More critically, many vendors bury consumer-unfriendly language in plain sight:
- Auto-renewal clauses buried on page 8 that renew your subscription automatically and make cancellation harder than signing up.
- Data monetization language that lets them use your information for AI training, marketing research, or resale to third parties.
- Liability waivers that cap their responsibility if they lose your data or experience a security breach.
- Forced arbitration that forces disputes into private arbitration and forbids class-action lawsuits.
- Unilateral change rights that let them modify pricing or terms mid-contract with minimal notice.
Key takeaway: A 15-minute terms review before signing can prevent months of regret, surprise charges, and lost data control.
The eight-point checklist for B2B SaaS terms
B2B SaaS Terms Review Checklist
Your progress is saved automatically in your browser.
1. Data Ownership and AI Training
Your data is your company's most valuable asset. Many SaaS vendors now claim the right to use your data, anonymized or otherwise, to train machine learning models, benchmark against competitors, or sell insights to other customers.
Red flags:- "We may use your data to improve our services" without specifying what "improve" means.
- "Anonymized or aggregated data" can be used for any purpose, with no opt-out.
- No explicit carve-out for AI training.
- A clear statement that you own 100% of the data you create and upload.
- A blanket prohibition on using your data for AI training, or at minimum, a requirement for explicit, written opt-in before any AI use.
- A clause that lets you request deletion of your data if you terminate the service.
2. Auto-Renewal and Cancellation
Auto-renewal is the leading cause of surprise charges and unwanted subscription locks. The Federal Trade Commission has cracked down on dark patterns that make cancellation intentionally hard, but many vendors still comply only technically, not in spirit.
Red flags:- Cancellation requires an email to support (which takes 5–10 business days to process).
- No in-app or web-based cancellation option.
- A requirement to contact sales or account management to cancel.
- No explicit confirmation email showing the cancellation is effective immediately.
- A promise that cancellation is "free and easy," and that you can cancel via the same method you used to sign up (self-service, one click).
- A guarantee that cancellation is effective immediately, or within 24 hours at most.
- No pro-rata refund language that penalizes you for canceling mid-month.
3. Liability and Indemnification
If a vendor loses your data or violates data-protection laws on your behalf, you need to know whether they'll cover the fallout. Many SaaS vendors cap their total liability at one month's subscription fees, which is often insufficient if they breach security.
Red flags:- Liability capped at "the lesser of $100 or one month's fees."
- Exclusions for "indirect, incidental, or consequential damages" that swallow most real-world harm (lost revenue, regulatory fines, notification costs).
- No indemnification clause requiring them to defend you if they're sued for violating a third party's IP or privacy rights.
- Liability capped at no less than 12 months of fees paid.
- Explicit indemnification promising the vendor will cover legal costs if they violate third-party rights or data laws on your behalf.
- A carve-out stating that liability caps do not apply to data breaches, security failures, or violations of data-protection laws like GDPR or CCPA.
4. Dispute Resolution and Arbitration
Forced arbitration clauses prevent you from suing in court, filing in small claims, or joining a class-action lawsuit. You're forced into private arbitration, which is often expensive, opaque, and favors the larger party (the vendor).
Red flags:- "Any dispute must be resolved through binding arbitration."
- "Class actions are waived."
- Arbitration must occur in the vendor's home state or country.
- No carve-out for injunctive relief (getting a court to stop illegal activity immediately).
- Either no arbitration clause at all, or explicit carve-outs for claims under GDPR, CCPA, CFAA, or other consumer-protection laws.
- A preserved right to pursue class actions or small-claims court.
- If arbitration is required, confirmation that either party can pursue emergency injunctive relief in court.
5. Pricing and Renewal Terms
Many SaaS vendors reserve the right to raise your price on renewal with as little as 30 days' notice. If you're locked into a 3-year term, you may have no practical escape route if they raise your bill 50%.
Red flags:- "Pricing may change at any time, effective upon renewal or as otherwise specified."
- No minimum notice period for price increases.
- No right to cancel if pricing increases above a certain threshold (e.g., >10% increase).
- Yearly price "true-ups" based on usage that aren't capped.
- A guarantee that pricing cannot increase during your initial term (at least 12 months).
- A requirement for 60+ days' notice before any price increase on renewal.
- A right to cancel at no penalty if pricing increases more than 10–15% and you choose not to accept the new price.
6. Security and Breach Notification
If a vendor stores your data and experiences a breach, you need a contractual promise that they'll notify you quickly and that they maintain a baseline security standard.
Red flags:- No mention of security standards or certifications.
- "We'll notify you of breaches as required by law" (which varies by state and is often vague).
- No commitment to a specific notification timeline (e.g., "within 48 hours").
- A commitment to maintaining SOC 2 Type II, ISO 27001, or equivalent security certification.
- A promise to notify you of breaches within 24–48 hours of discovery.
- A clause confirming they'll cover the cost of breach notifications if the breach is their fault.
7. Term Length and Termination Rights
Longer terms lock you in. A 3-year agreement is much riskier than a 12-month agreement, because the vendor's product may degrade, your needs may change, or the company may go out of business.
Red flags:- Initial term is longer than 12 months.
- Auto-renewal with a longer term (e.g., renews into a 2-year term if you don't cancel 60 days before renewal).
- Either party can terminate only "for cause" (breach), not "for convenience" (any reason).
- Initial term of 12 months or less.
- Auto-renewal into a 12-month term (not longer).
- A right for either party to terminate for convenience with 30 days' notice.
8. Acceptable Use and Suspension Rights
Vendors need to reserve the right to suspend accounts that violate laws or their terms. But they should have to notify you first and give you a chance to fix the issue, unless the violation is severe (illegal content, active fraud).
Red flags:- "We may suspend your account immediately and without notice for any reason we deem appropriate."
- No distinction between minor violations (technical support abuse) and serious ones (illegal activity).
- Suspension language that's vague (e.g., "inappropriate use" without definition).
- A promise to give notice and at least 5–10 business days to cure non-serious violations before suspension.
- A clear list of suspension triggers (illegal activity, repeated breach after notice, etc.).
- A right to retrieve your data before or immediately after suspension.
How to use this checklist in practice
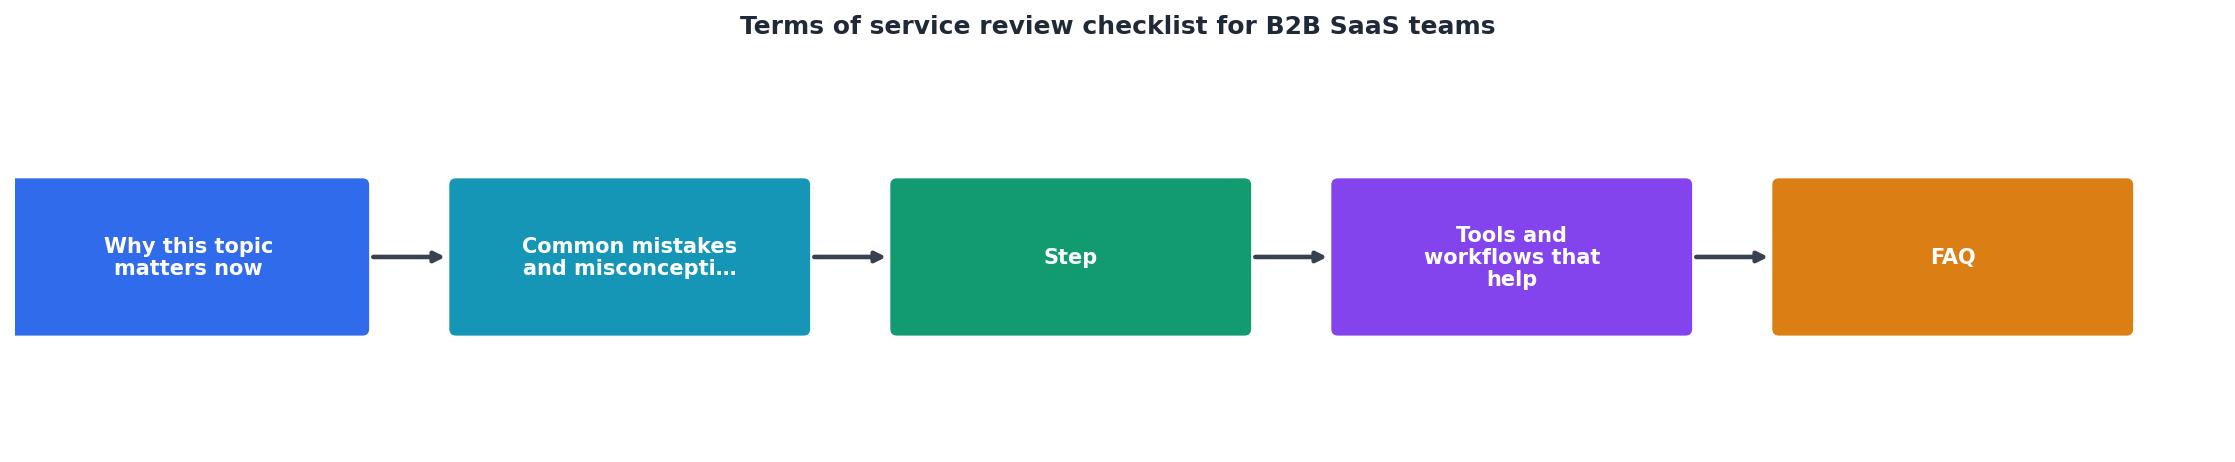
Step-by-step workflow
- Download the checklist and open the vendor's terms of service side-by-side.
- Search for keywords in the terms: "data," "AI," "training," "arbitration," "auto-renewal," "cancel," "liability," "suspension."
- Go through each checklist item and mark it pass, fail, or "needs negotiation."
- Flag failures and negotiation items for your legal or procurement team.
- Use the results to decide: Do you sign as-is, negotiate before signing, or look for an alternative vendor?
Red-flag negotiation points
If a vendor has one or two failures, they may be willing to negotiate. Here's the priority order for negotiation:
- Data ownership and AI training (non-negotiable for most teams).
- Auto-renewal and easy cancellation (federal law increasingly requires this).
- Liability cap (especially for security breaches).
- Arbitration clause (consider it a dealbreaker if the vendor handles sensitive data).
When to use Terms Doctor
The Terms Doctor browser extension automates the first step: it finds the terms of service on any website and runs 101 consumer-protection checks automatically. It grades the terms A–F, highlights specific red flags, and lets you compare versions to see what changed at renewal. For B2B teams reviewing 10+ vendor contracts per year, Terms Doctor cuts review time from 30 minutes per vendor to 3 minutes, and catches clauses you'd likely miss in a manual read.
FAQ
Frequently Asked Questions
Protect your team with a process, not just a checklist
Reading terms once and signing is not enough. A mature SaaS procurement process includes:
- A centralized contract repository where all signed SaaS agreements are stored and searchable.
- Annual renewal audits where your team re-reviews top 10–20 vendors for term changes and pricing opportunities.
- A red-flag response playbook defining which terms you'll negotiate for and which are dealbreakers.
- A tool like Terms Doctor integrated into your procurement workflow to flag high-risk clauses on every new vendor.
Get a faster terms review with Terms Doctor
Reading and interpreting 10,000+ words of legal prose is not a good use of your time. The free Terms Doctor browser extension finds terms of service on any website and runs 101 consumer-protection checks instantly, scanning for forced arbitration, hidden auto-renewal clauses, unlimited liability waivers, AI training clauses, and 97 other red flags. You get an A–F grade, a plain-language summary, and side-by-side change tracking so you can see exactly what changed at renewal. Install it free on Chrome, Edge, Brave, Opera, or Vivaldi, and never skip a terms review again. (Remember: automated checks are not legal advice; have a lawyer review critical agreements before you sign.)
Additional Resources
- SaaS Agreement Checklist: 23 Things to Review in Every ... - Evaluate SaaS agreement and contracts using this checklist based on SaaS management straegies for licenses, renewls, and cost monitoring.
- SaaS Contract Review Checklist: 12 Clauses - 1. Does the scope clearly describe the service and implementation?2. Are fees, usage charges, and price changes predictable?3. How do renewal ...
- Checklist: Practical considerations when reviewing and ... - The checklist addresses the following steps: Pre-contract considerations; Review the SaaS terms and conditions; Review the order forms and schedules; Consider ...
Ready to Read Terms Before You Sign?
Terms Doctor finds terms of service on any site and grades them A-F in seconds.
Get Started“Terms Doctor flagged forced arbitration and AI training clauses in seconds. I finally know what I am agreeing to.”
Privacy-conscious shopper