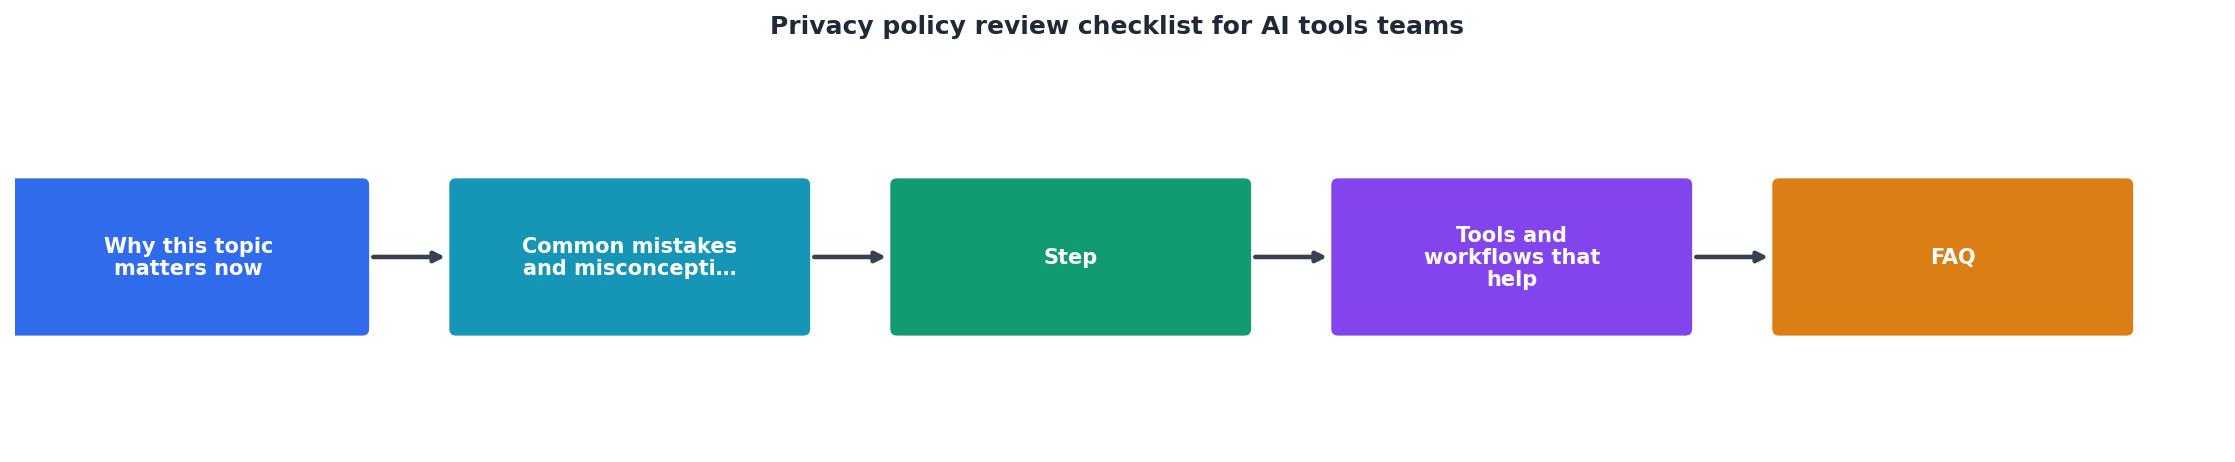
Privacy policy review checklist for AI tools teams
When your team adopts a new AI tool, whether it's ChatGPT for content generation, Slack for team communication, or Notion for project management, you're entering a contract that most people never read. Privacy policies and terms of service for AI tools are notoriously dense, filled with jargon, and often contain hidden provisions that expose your company, clients, or users to risk. This checklist helps your team review these documents quickly, spot red flags, and make informed decisions before s
Photo by Vlad Deep from Pexels
When your team adopts a new AI tool, whether it's ChatGPT for content generation, Slack for team communication, or Notion for project management, you're entering a contract that most people never read. Privacy policies and terms of service for AI tools are notoriously dense, filled with jargon, and often contain hidden provisions that expose your company, clients, or users to risk. This checklist helps your team review these documents quickly, spot red flags, and make informed decisions before signing up.
TL;DR
- AI tools may train on your data, sell access to third parties, or use weak encryption, read the privacy policy before adoption.
- Create a cross-functional review team (legal, security, product, compliance) to assess risk across multiple dimensions.
- Look for specific red flags: forced arbitration, auto-renewal clauses, data retention policies, and AI training opt-outs.
- Use automated tools like Terms Doctor to speed up the review process and compare multiple vendor policies side by side.
- Document your review findings and maintain a living record of policy changes over time.
Why AI tools need extra scrutiny
AI tools are fundamentally different from traditional SaaS applications. When you type into ChatGPT, Copilot, or Claude, your input is often used to train the model itself, meaning your proprietary information, customer data, or sensitive business processes become part of a machine learning system that the vendor may use or resell. Unlike a spreadsheet tool that simply stores your data, an AI tool ingests it, learns from it, and changes how it behaves based on it.
- Data usage for model training – Whether your inputs are used to improve the AI model globally.
- Third-party data sharing – Which partners, researchers, or advertisers get access to anonymized (or not-so-anonymized) data.
- Lack of deletion guarantees – What happens when you ask the vendor to delete your data; many refuse.
- Forced arbitration – Clauses that prevent you from suing and force disputes into private arbitration.
- Auto-renewal traps – Automatic billing renewal with hard-to-find cancellation policies.
Building your review team
The most effective privacy policy reviews happen when multiple perspectives join the conversation. A single reviewer, even a lawyer, can miss risks that a security engineer or product manager would catch immediately. Here's how to staff your team:
Core review roles
- Legal or compliance lead – Responsible for contract terms, liability limits, indemnification, and dispute resolution.
- Security/IT lead – Evaluates encryption standards, access controls, audit rights, and incident response requirements.
- Product/business owner – Assesses whether the tool's capabilities justify the privacy trade-offs and identifies functional deal-breakers.
- Data steward or privacy officer – Reviews data retention, deletion policies, and regulatory compliance (GDPR, CCPA, HIPAA, etc.).
Decision-making process
Define upfront who has veto power. Does legal have final say, or does your team vote? Does security need to approve? Having clear authority prevents scope creep and endless debate.
The privacy policy review checklist
Privacy Policy Review Checklist for AI Tools
Your progress is saved automatically in your browser.
"The security of our customers' personal information and data is critical to everything we do.">, Privacy.com Virtual Cards
Step-by-step review process
Step 1: Gather baseline documentation
Before your team starts reviewing, collect all relevant documents:- The vendor's current privacy policy (download and date-stamp it).
- Terms of service and acceptable use policy.
- Data processing agreement (DPA) or data security addendum if available.
- Security certifications (SOC 2 Type II report, ISO 27001, etc.).
- Any public statements or documentation about data retention and model training.
Step 2: Run an automated check first
- Forced arbitration and class action waivers
- Auto-renewal and cancellation difficulty
- Data retention and AI training opt-outs
- Liability caps and indemnification
- Regulatory compliance gaps
Step 3: Assign sections to domain experts
Divide the policy into sections and assign each to a team member based on expertise:- Legal: Liability, indemnification, dispute resolution, warranties
- Security: Encryption, access controls, audit rights, incident response
- Product: Feature parity, data usage, service availability
- Compliance: GDPR/CCPA compliance, data retention, subprocessor management
Step 4: Hold a synchronous review meeting
Bring the team together (in person or async, depending on your culture) to discuss findings:- Highlight red flags from each section.
- Discuss trade-offs: Does the tool's value justify accepting the risks?
- Identify negotiation opportunities (e.g., requesting a data processing addendum or stronger encryption requirements).
- Make a go/no-go decision or identify what needs to change before adoption.
Step 5: Document and monitor
- Tool name and vendor
- Review date and reviewers
- Key risks identified
- Final decision (approved / approved with conditions / rejected)
- Link to the policy version reviewed
- Date of next re-review
Common red flags in AI tool policies
- No opt-out for AI training: The tool trains on your data with no way to disable it.
- Blanket third-party data sharing: Data is shared with "partners" or "service providers" with no limits or transparency.
- Unlimited liability caps: The vendor's liability is capped at $0 or fees paid (with no exceptions for data breaches).
- Unilateral policy changes: The vendor can change terms without notice or only with email notification.
- Forced arbitration + class action waiver: You cannot sue; disputes go to arbitration, and you cannot join a class action.
- No data deletion guarantee: Backups or "residual data" are kept indefinitely even after deletion requests.
Using Terms Doctor to speed up reviews
Terms Doctor is a free browser extension for Chrome, Edge, Brave, Opera, and Vivaldi that automatically discovers privacy policies and terms of service on any website and runs 101 consumer-protection checks. Here's how it helps your team:
- Auto-discovery: Visit the vendor's website, and Terms Doctor highlights where the privacy policy lives (many vendors hide it in the footer).
- Instant grading: Get an A–F grade for the policy before your team spends an hour reading it.
- Red-flag highlights: The tool marks clauses related to forced arbitration, auto-renewal, AI training, and other key risks.
- Side-by-side comparison: Compare two vendors' policies directly to see which has stronger privacy protections.
- Change tracking: Monitor when a vendor updates their policy and get notified of material changes.
- Exportable reports: Generate a PDF summary to share with stakeholders or attach to your compliance file.
FAQ
Frequently Asked Questions
Get started with your review today
Reviewing privacy policies and terms of service doesn't require a law degree, it requires a disciplined process and the right tools. Start with the checklist above, assemble your cross-functional team, and use Terms Doctor to surface risks fast. Your future self will thank you when you avoid adopting a tool with a hidden forced-arbitration clause or an auto-renewal trap.
Download the free Terms Doctor extension for Chrome, Edge, Brave, Opera, or Vivaldi today. When you visit any vendor's website, Terms Doctor automatically finds their privacy policy, runs 101 consumer-protection checks, assigns a clear A–F grade, and highlights red flags. Use it to kick off your team's next vendor review, and build a library of review decisions you can share and refine over time. Note: Terms Doctor's automated checks are not legal advice; always consult your legal team for final decisions on vendor adoption and contract negotiations.
Additional Resources
- Privacy.com Virtual Cards – Secure, Temporary Cards - Protect your financial life with Privacy.com Virtual Cards. Create secure, temporary card numbers to prevent fraud and control your online spending.
- Google Privacy Policy - We build security into our services to protect your information · We use encryption to keep your data private while in transit · We offer a range of security ...
- Privacy - Privacy is the ability of an individual or group to seclude themselves or information about themselves, and thereby express themselves selectively.
Ready to Read Terms Before You Sign?
Terms Doctor finds terms of service on any site and grades them A-F in seconds.
Get Started“Terms Doctor flagged forced arbitration and AI training clauses in seconds. I finally know what I am agreeing to.”
Privacy-conscious shopper